Vulnerability intelligence
Decide which vulnerabilities matter, and what to do next.
Rapid Risk Radar helps security teams turn noisy vulnerability data into prioritized, actionable intelligence — delivered through a dashboard, alerts, and an API.
Free tier, no card required. The community edition stays free.
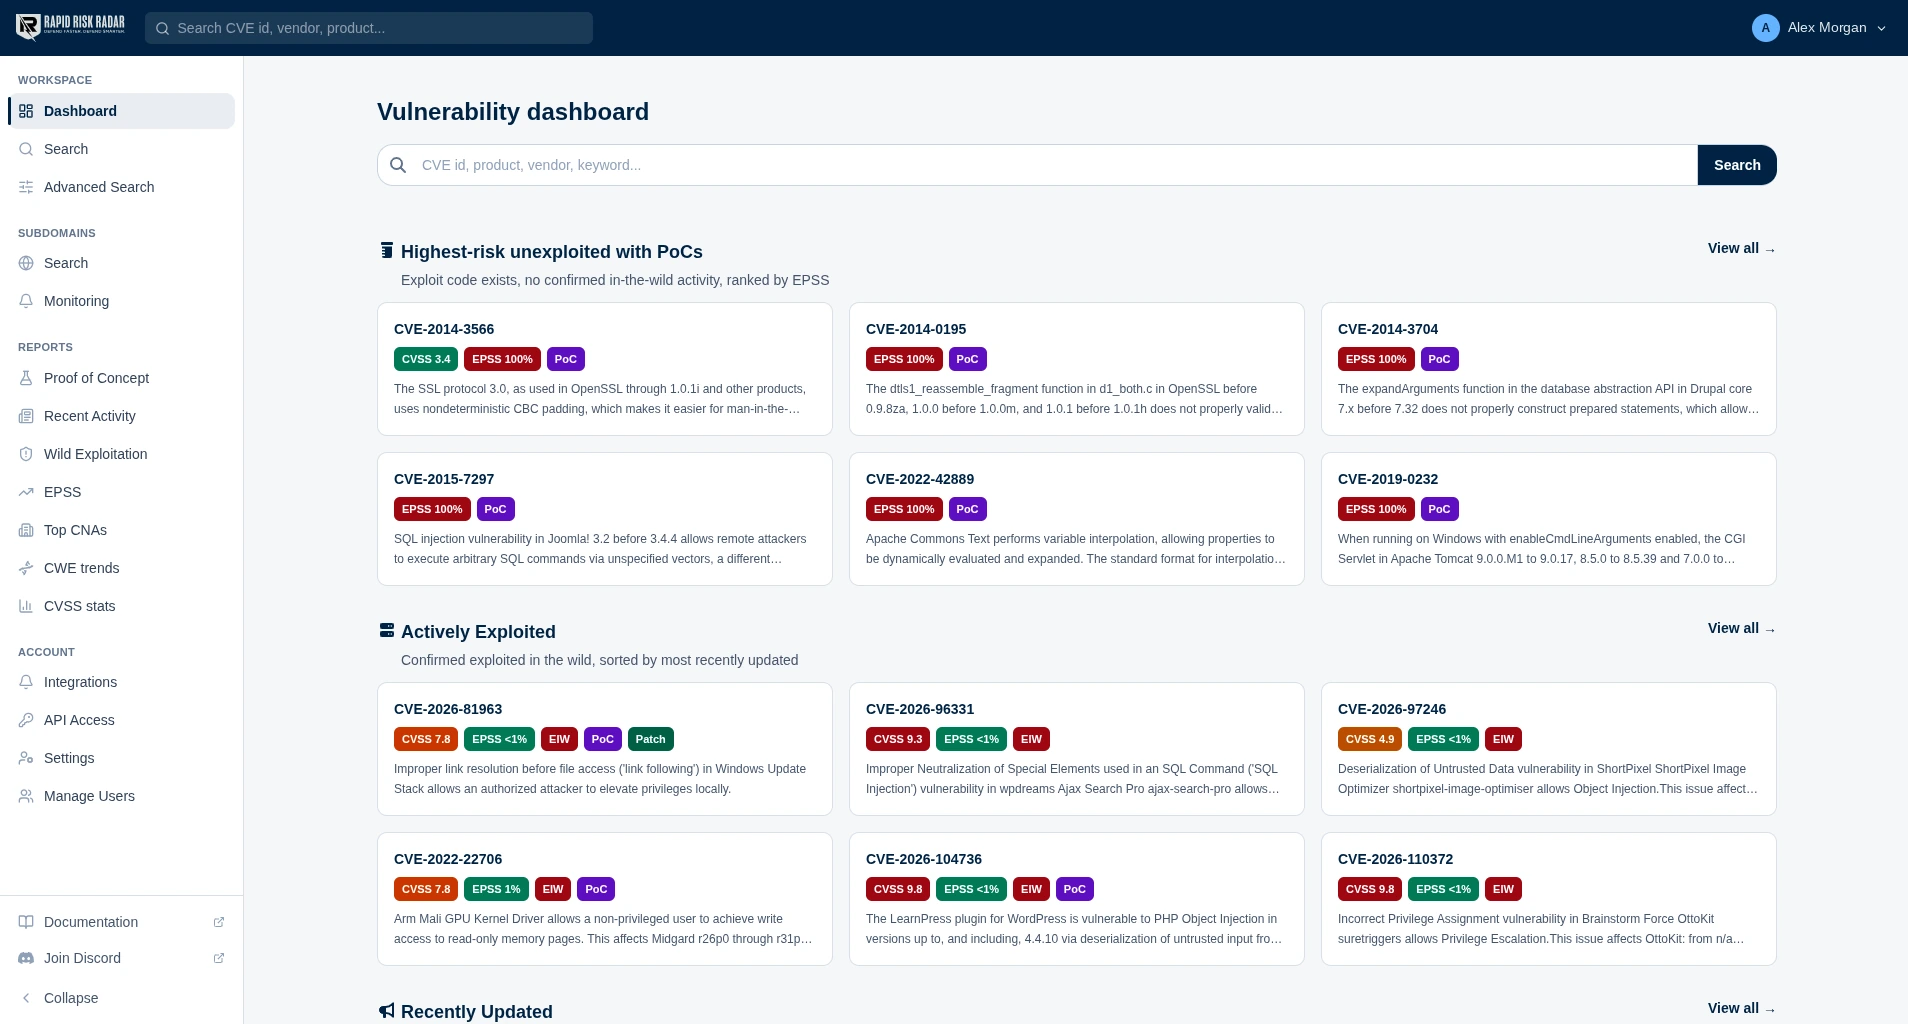
For SOC & vulnerability management
Thousands of CVEs. A handful that matter today.
Your scanner tells you what is present. Rapid Risk Radar tells you what is being exploited, what has public proof-of-concept code, and what is worth interrupting the patch cycle for.
See how prioritization works| # | CVE | CVSS | EPSS | Signals |
|---|---|---|---|---|
| 1 | CVE-2025-53771 | 6.5 | 100% | PoCPatch |
| 2 | CVE-2022-42889 | — | 100% | PoC |
| 3 | CVE-2014-3566 | 3.4 | 100% | PoC |
| 4 | CVE-2026-105105 | 9.8 | <1% | PoC |
| 5 | CVE-2026-22747 | 6.8 | <1% | PoC |
Not a scanner. The layer that decides what your scanner found.
Rapid Risk Radar sits between the tools you already own and the decisions your team has to make. That is a narrower job than most security platforms claim, and it is the reason it fits alongside all of them.
Rapid Risk Radar is
- A vulnerability intelligence aggregation platform
- A dashboard for analysts and decision makers
- An API service for enrichment and automation
- A monitoring and alerting layer for CVE, technology, vendor, product, brand, and CT certificate signals
Rapid Risk Radar is not
- A vulnerability scanner
- A patch management product
- A SIEM, SOAR, or ticketing replacement
- A certificate lifecycle management platform
- A license to redistribute data, unless OEM terms are in place
How it works
Aggregate. Prioritize. Deliver.
Three moves, in that order. Everything else the platform does is in service of one of them.
Aggregate
Many vulnerability sources, not one. CVE records, vendor advisories, exploit databases, public chatter, and Certificate Transparency logs land in one place — so a delay or outage upstream does not blind your team.
Prioritize
Exploit context, PoC links, KEV relevance, trending signals, and keyword weighting turn a severity score into an operational decision. Filter presets and SBOM support narrow the field to your estate.
Deliver
Review as a team in the dashboard, push alerts to Slack, Discord, or a webhook, and enrich your SIEM, SOAR, VM, and ticketing workflows through the API. The intelligence arrives where the work already happens.
Four surfaces
One platform. Four ways it reaches you.
Web Dashboard
Human investigation and visualization for analysts and decision makers. Graphs, tables, and trends, advanced filtering with keyword weights, PoC links, public chatter analysis, and the ability to mark and review CVEs as a team.
Enterprise API
Internal workflow enrichment for the licensed customer. Feed SOC, SOAR, SIEM, and VM integrations, automate triage, and keep vulnerability context flowing into the tools your team already runs.
CT Certificate Monitoring
NewCertificate Transparency logs surface new subdomains, third-party infrastructure, test environments, and brand-adjacent activity. Search is free and public. Every plan can save domain monitors, and paid plans watch more domains.
OEM / White-Label Feed
For security product companies, MSSPs, and data platforms embedding RRR intelligence into another product, customer portal, or downstream managed service. Licensed and sized in Feed Units.
New with this release
Certificate Transparency, added.
Every certificate issued for a public domain lands in a Certificate Transparency log. That is a live feed of new subdomains, third-party infrastructure, forgotten test environments, and anything issued in your name that you did not ask for.
| # | Subdomain | Depth | Signals |
|---|---|---|---|
| 1 | staging-api..com | 3 | New |
| 2 | vpn2.eu..com | 4 | New |
| 3 | *.dev..com | 4 | Wildcard |
| 4 | auth..com | 3 | |
| 5 | status..com | 3 | |
| 6 | mail..com | 3 |
Search is free and public.
Look up every name logged in certificates for any domain. No account, no license — it stays open.
Monitoring starts on the free plan.
Watch the domains you care about. Every new name logged for them is recorded for you to review, and paid plans watch more domains.
Example data, shown as the subdomain search lists it.
Sound familiar?
If you have said one of these out loud this quarter.
These are the sentences that bring teams to Rapid Risk Radar. Find yours, and the rest of the conversation is short.
- “We cannot keep up with CVEs.”Prioritization with exploit context, PoC visibility, and a shared workflow that SOC and IT can both agree on.
- “We need vulnerability data inside our tools.”API access for enrichment, automation, and integration into the systems your team already runs.
- “We need to build detection content or advisories.”Security content prioritization with source tracking, PoC links, and real-world exploitation signals.
- “We need to track vulnerabilities tied to our products or brand.”Company and product monitoring, review workflow, reporting, and API integration into PSIRT processes.
- “NVD delays or outages create operational risk for us.”An alternate aggregated intelligence source with API continuity, so one upstream feed is never a single point of failure.
- “We want to know when new certificates appear for our domains.”Certificate log search, plus saved domain watches that record every new name.
- “We are putting this data into our product or customer portal.”An OEM feed license sized in Feed Units, with contract-defined downstream rights.
Use cases
Eight jobs. One platform underneath.
Vulnerability intelligence stops being abstract the moment it maps to a job someone is already accountable for. Here are the eight we see most.
Security Operations
- SOC + Vulnerability ManagementPrioritize real risk instead of chasing every CVE with equal urgency.When: Too many CVEs, unclear exploitability, patching debatesWho buysCISOSOC DirectorVM ManagerIT OpsSecEng
- Operational ResilienceA second aggregated source, so one upstream feed never blinds you.When: NVD or upstream feed delays, outages, or data quality concernsWho buysSecurity ArchitectureVMSOCCompliance
Threat Intel
- Threat Intel + Situational AwarenessContinuous monitoring of the vendors and technologies you rely on.When: Need early awareness of trending CVEs and exploit activityWho buysThreat Intel LeadSOC ManagerSecurity Leadership
- Product + Detection EngineeringA defensible way to prioritize research and security content work.When: Need to decide which CVEs require signatures, rules, or advisoriesWho buysProduct SecurityDetection EngineeringThreat Research
PSIRT & Compliance
- PSIRT, Compliance + Brand MonitoringMonitoring and review workflows that double as compliance evidence.When: Need to track vulnerabilities tied to company, products, or brandWho buysPSIRT LeadGRCProduct SecurityLegal/Comms
- CT Certificate Search + MonitoringFree search, plus domain monitoring that grows with your plan.When: Need to know when certificates are issued for their domainsWho buysSOCBrand ProtectionASMInfraProduct Security
MSSP & OEM
- Red Teams, Consultants + MSSPsRepeatable research and prep across many customer environments.When: Need faster vulnerability and PoC research across engagementsWho buysConsulting LeadRed Team LeadMSSP Practice Lead
- OEM / White-Label FeedA Feed Unit license with contract-defined redistribution rights.When: Need vulnerability intelligence inside another productWho buysSecurity Product LeadData Platform LeadEngineering Leadership
Wear more than one hat? These are four ways into the same platform, not four different products. Pick whichever description fits you best — the platform does not change.
Plans
Start free. Grow into the rest.
Every plan runs on the same intelligence. What changes is how much of the workflow, automation, and deployment control comes with it.
Community
A working taste of the platform for anyone not ready to commit. Full CVE database, filters, chatter, and visualizations.
Start freeResearcher
The full research surface: PoC links, keyword weighting, API access, SBOM support, and alerting.
Talk to usBusiness
Everything in Researcher, plus user management, dedicated or self-hosted deployment, and integration with your existing stack.
Talk to sales| Feature | Community | Researcher | Business |
|---|---|---|---|
| Intelligence | |||
Database access The full CVE database and its sources | |||
CVE filters Filter vulnerabilities by any criteria | |||
Public chatter What the internet is saying about trending CVEs | |||
Data visualization Customizable graphs and tables | |||
PoC links Links to public proof-of-concept code | |||
Keyword weights Prioritize CVEs with weighting you control | |||
| Workflow | |||
Mark as reviewed Track what your team has already triaged | |||
Filter presets Save and reuse filter configurations | Up to 5 | Unlimited | |
SBOM support Automatic filter creation from SBOM uploads | |||
Alerts Slack, Discord, and webhook delivery | |||
API access Automate your workflows against our data | Included | Unlimited | |
| Certificate Transparency | |||
CT certificate searchNew Every name in logged certificates for a domain, or by keyword | |||
CT monitoringNew Watched domains, with every new name recorded | 1 domain | 25 domains | 250 per seat |
| Deployment & team | |||
User management Add, remove, and manage your team | |||
Dedicated server Run Rapid Risk Radar on infrastructure you control | |||
Choose your cloud Pick where the platform is hosted | |||
Existing solution integration Connect to your asset or vulnerability management tooling | |||
Support Help when you need it | Discord community | Prioritized + feature requests | Custom SLA |
Every plan is customizable. What you need, how it is deployed, and how it is supported are all part of the conversation — reach out and we will scope it with you.
Partners
Built alongside the people who deploy it.
Rapid Risk Radar works with security consultancies who bring vulnerability intelligence into real engagements. Interested in reselling or embedding the platform?
SolaSec
A Dallas-based consulting firm with a singular focus on cybersecurity, working with organizations to identify vulnerabilities and strengthen defenses.
CyberDagger
A veteran-owned offensive security firm that builds its own tooling, discovers vulnerabilities, and simulates real-world adversaries against client defenses.
The weekly digest
The CVEs that mattered, every week.
A short rundown of the week's exploited vulnerabilities, supply chain incidents, and the patches worth interrupting your sprint for. No product pitches.
Decide what matters. Before it decides for you.
Start on the free community edition, or talk to us about an enterprise license, CT monitoring, or an OEM feed for your product.
No card required. The community edition is free.